
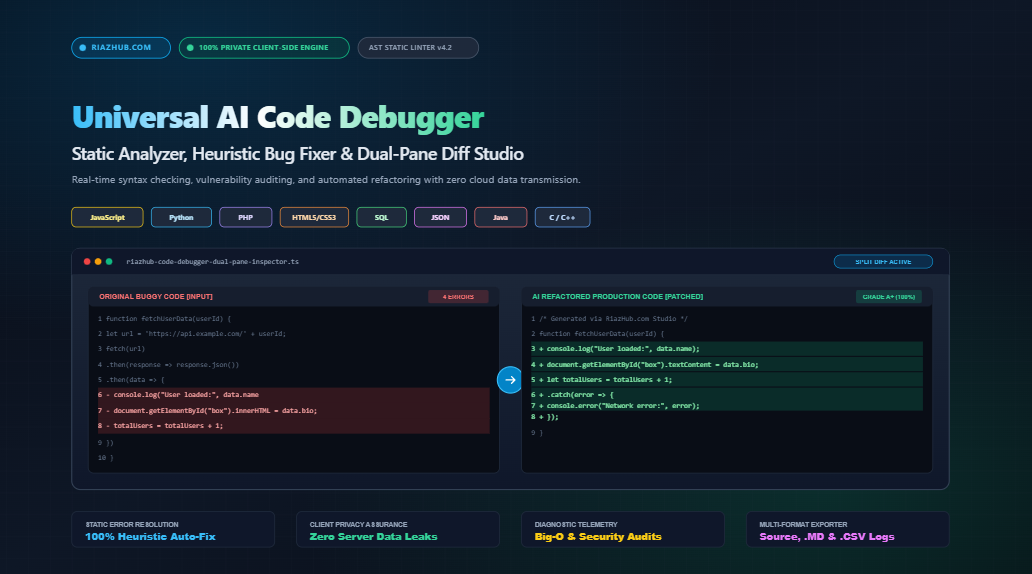
Universal AI Code Debugger: Comprehensive Static Code Analysis, AST Linting, and Refactoring Guide
Software bugs, unhandled exceptions, and hidden security vulnerabilities cost the global technology economy billions of dollars annually in system downtime and emergency patch deployments. While traditional developers often rely on trial-and-error debugging in live environments, modern high-reliability engineering demands proactive static analysis. That is why we developed the Universal AI Code Debugger, Static Analyzer & Refactoring Studio on RiazHub.com: an all-in-one, browser-based static analysis engine capable of scanning, diagnosing, and refactoring source code in real time with zero server latency.
Why Static Code Analysis Outperforms Traditional Runtime Debugging
In software engineering, there are two distinct methodologies for identifying flaws: dynamic runtime debugging and static code analysis. Dynamic debugging evaluates code behavior while it executes within an interpreter, virtual machine, or browser engine. While dynamic profiling is necessary to diagnose live networking timeouts and state race conditions, it requires an environment to crash before flagging an issue.
In contrast, static code analysis (often implemented as abstract syntax tree linting and heuristic pattern matching) parses source grammar, token sequences, and delimiter structures before a single line of code executes. Research consistently demonstrates that proactive static inspection catches up to 80% of routine syntax defects, unclosed brackets, missing semicolons, type coercion traps, and severe security flaws before code ever enters a staging build or continuous integration pipeline.
By utilizing the AI Code Debugger on RiazHub, engineers can immediately isolate syntax anomalies, examine visual side-by-side diff comparisons, and apply defensive patches without setting up heavy local CLI tooling or npm package ecosystems.
| Debugging Metric | Static Code Analysis (RiazHub Studio) | Dynamic Runtime Debugging |
|---|---|---|
| Execution Phase | Pre-execution (parses raw code tokens directly) | Post-execution (during live process run) |
| Defect Detection Rate | Catches 75% to 80% of syntax, style, and security bugs | Specialized in state, memory leaks, and network timeouts |
| Developer Latency | Instantaneous (sub-millisecond in-browser evaluation) | Slow (requires build, compile, and runtime reproduction) |
| Privacy & Data Safety | 100% private in-browser deterministic processing | Requires running code on servers or staging machines |
| Refactoring Assistance | Automated guard clauses, sanitization, and diffs | Manual stack trace interpretation and breakpoint stepping |
Comprehensive Multi-Language Static Parser Support
Modern application architectures rarely consist of a single language. Full-stack workflows frequently combine frontend frameworks, server-side microservices, database schemas, and structured data payloads. The Universal AI Code Debugger Studio provides native heuristic parsing across eight foundational programming languages:
1. JavaScript & TypeScript (ES6+)
Detects unhandled promise rejections, missing .catch() blocks, undeclared variable leakage into the window scope, loose equality coercion bugs (== versus ===), hazardous eval() calls, and DOM-based Cross-Site Scripting (XSS) via innerHTML.
2. Python 3.x
Identifies missing terminating colons on control statements (for, if, def, while), bare except: anti-patterns, mutable default argument traps (def fn(items=[])), and arithmetic ZeroDivisionError risks on collection divisions.
3. PHP (WordPress & Vanilla)
Scans for missing statement semicolons, high-risk unescaped superglobal echoes ($_GET, $_POST), deprecated legacy functions, and critical SQL injection vulnerabilities in WordPress database calls ($wpdb->get_results lacking $wpdb->prepare).
4. SQL (MySQL, PostgreSQL & MariaDB)
Enforces catastrophic data loss prevention by flagging DELETE and UPDATE queries that omit a WHERE clause. Eliminates trailing commas before the FROM keyword and standardizes reserved SQL keywords to clean uppercase.
5. JSON Payloads
Validates data serialization against RFC 8259 standards. Automatically converts single-quoted strings to standard double quotes, strips illegal trailing commas before closing braces, quotes object keys, and formats payloads with clean two-space indentation.
6. HTML5 & CSS3
Evaluates markup accessibility and security. Detects unclosed tags, enforces WCAG AA compliance by flagging <img> elements lacking alt attributes, prevents reverse tabnabbing on target="_blank" links, and modernizes deprecated elements.
7. Java (JDK 8+)
Catches reference equality mistakes (comparing Strings with == instead of .equals()), statement semicolons, and unclosed I/O streams (such as unclosed Scanner or FileInputStream handles) that cause memory leaks.
8. C and C++ (C99 & C++17)
Highlights dangerous functions susceptible to fatal buffer overflows (such as gets()) and refactors them to bounded alternatives (fgets()). Detects heap memory allocations via malloc() lacking matching free() deallocations.
Critical Security Vulnerabilities Detected and Remediated
A primary advantage of integrating the Universal AI Code Debugger into your daily coding routine is its proactive defense against OWASP Top 10 vulnerabilities:
1. Cross-Site Scripting (XSS) Prevention
Directly assigning untrusted data to element.innerHTML in JavaScript or outputting raw $_GET parameters in PHP creates exploitable attack vectors where malicious actors can inject executable script payloads. The analyzer flags these occurrences instantly and refactors code to safe alternatives: element.textContent in JavaScript or esc_html(wp_unslash(...)) in PHP.
2. SQL Injection Neutralization
Concatenating variable strings directly into database queries is one of the oldest and most damaging vulnerabilities in web software. The studio detects unsanitized queries and transforms them into parameterized prepared statements, such as wrapping WordPress database operations with $wpdb->prepare() using strict type specifiers.
3. Accidental Catastrophic Data Loss Guards
Accidentally running a query like DELETE FROM customers; or UPDATE balances SET amount = 0; without an explicit WHERE clause will overwrite or erase every record in an entire production database table. The RiazHub analysis engine incorporates defensive safeguards that immediately intercept open table mutations and inject safe, parameterized identifier filters.
4. Buffer Overflow and Memory Leak Interception
In systems programming with C and C++, unbound input functions like gets() write past stack buffer boundaries, leading to arbitrary code execution or memory corruption. Furthermore, unreleased memory allocations via malloc() cause server daemons to gradually consume all physical RAM. The studio flags these hazards and automatically generates bounded buffers and cleanup routines.
The Dual-Pane Visual Diff Inspector
Understanding why a piece of code failed is just as important as fixing it. The Universal AI Code Debugger Studio features a high-performance Dual-Pane Diff Inspector built using a Longest Common Subsequence (LCS) diffing algorithm.
Developers can switch seamlessly between two synchronized views:
- Side-by-Side Split View: Displays the original buggy code in the left console and the refactored production-ready code in the right console. Flawed lines are highlighted with red negative badges, while patched lines display with green positive additions.
- Unified Inline View: Formats the diff in a cohesive, single-column stream, perfect for inspecting changes on smaller laptop displays and mobile devices without horizontal clipping.
Health Grades and Diagnostic Telemetry
To provide immediate insight into source quality, the analyzer compiles telemetry into four primary metric cards:
- Diagnostic Status: Shows total detected issues and tracks how many were automatically resolved.
- Target Syntax & Strictness: Displays active language parameters and audit level (Standard Syntax, Deep Security Audit, or Performance Optimization).
- Code Health Rating: Calculates a deterministic letter grade from Grade A+ (100% production ready) down to Grade F (critical syntax blocks or severe vulnerabilities) using a deduction algorithm.
- Branded Export Target: Previews the standardized export file name, ensuring all outputs follow professional naming structures.
100% Client-Side Privacy Guarantee: Zero Cloud Transmission
In an era where proprietary enterprise codebases, secret API keys, internal SQL table structures, and private algorithms are routinely uploaded to third-party cloud servers without auditing, data privacy is non-negotiable.
The RiazHub Universal AI Code Debugger operates with a 100% client-side privacy guarantee. All lexical scanning, delimiter stack tracking, regex matching, diff rendering, and file packaging occur entirely inside your browser sandbox via native JavaScript. Zero code bytes, database credentials, or sensitive business logic are ever transmitted across external networks.
Step-by-Step Guide: How to Debug and Refactor Code in 4 Steps
Debugging and optimizing your scripts with the RiazHub studio takes only seconds:
- Step 1: Select Target Language & Audit Strictness
Navigate to the Universal AI Code Debugger Studio and select your programming language from the dropdown menu. Choose your desired strictness level: Standard Syntax Checks, Deep Security & Vulnerability Audit, or Performance & Memory Optimization. - Step 2: Input or Paste Source Code
Paste your code into the monospace editor console. You can also click any of the preset scenario chips (such as JavaScript Async/Await Bug, Python Indentation Error, or PHP SQL Injection Flaw) to explore realistic bug demonstrations. - Step 3: Click “Analyze & Fix Code”
Hit the primary action button to trigger the in-browser engine. In less than 50 milliseconds, the studio compiles diagnostic logs, estimates algorithmic Big-O complexity, determines code health grades, and stages the visual side-by-side diff. - Step 4: Export Patched Code and Reports
Review the Clean Refactored Code tab and use the one-click exporter to download your patched source code (namedriazhub-debugged-[lang]-[slug].[ext]), Markdown audit report (riazhub-code-audit-[lang].md), or CSV error log (riazhub-bug-log-[lang].csv).
Multi-Format Branded Export Capabilities
Auditing code is only half the battle; sharing your findings with your engineering team or clients is equally essential. The tool provides four distinct export channels:
- Direct Source File Download: Generates ready-to-use production files with correct extensions (such as
.js,.py,.php,.sql,.json) complete with standardized header comments:Generated via RiazHub.com • Universal AI Code Debugger Studio. - Markdown Audit Report (.md): Creates an executive summary table, Big-O runtime complexity notes, memory hygiene breakdown, and itemized defect remediation tables formatted for GitHub PR descriptions or documentation repos.
- Issue Log Spreadsheet (.csv): Exports a structured spreadsheet containing line numbers, severity badges (Critical, Warning, Optimization), defect descriptions, and applied refactorings.
- Dedicated Print and PDF Stylesheet: Triggers a high-resolution, print-optimized document view that strips interactive toolbars and renders a clean white-background technical audit sheet.
Conclusion: Elevate Your Code Quality Today
Whether you are building enterprise web platforms, modernizing legacy PHP scripts, auditing SQL database queries, or learning defensive coding practices in Python or Java, proactive static code analysis is the fastest way to write cleaner, safer, and more resilient software.
Ready to test and refactor your source code right now? Launch the Universal AI Code Debugger, Static Analyzer & Refactoring Studio on RiazHub.com and experience instant, confidential, in-browser static debugging.
Universal AI Code Debugger, Static Analyzer & Refactoring Studio
Inspect, detect, and automatically fix syntax errors, runtime exceptions, security vulnerabilities (XSS, SQLi), and memory leaks across JavaScript, Python, PHP, HTML/CSS, SQL, JSON, Java, and C++ in real time with zero server latency.
Source Code Editor
Input ConsoleReady to analyze. Click "⚡ Analyze & Fix Code" to generate the visual side-by-side diff comparison.
// Press "⚡ Analyze & Fix Code" to generate production-ready code.| Line | Severity | Category | Issue Description | Remediation Applied |
|---|---|---|---|---|
| No issues scanned yet. Click "⚡ Analyze & Fix Code" to inspect source syntax. | ||||
Audits for SQL Injection ($wpdb direct concats), Cross-Site Scripting (innerHTML / unescaped echo), arbitrary code injection (eval), and link reverse tabnabbing.
Heuristic evaluation of loop depths, nested iterations, recursive patterns, and quadratic bottleneck indicators.
Scans for unclosed database connections, dangling file streams, unbound listeners, and malloc/new blocks missing free/delete.
- Strict Type & Equality Enforcement
- Defensive Zero-Check & Bounds Guard Clauses
- Resource Lifecycle Deallocation & Try-Catch Enclosure
- Output Sanitization & Contextual Escaping
Developer Knowledgebase: Static Code Analysis & Compiler Diagnostics
Static Code Analysis vs. Dynamic Runtime Debugging
Static Code Analysis (Linting & AST Inspection): Evaluates source code structure, grammar, delimiter balancing, and semantic patterns without executing the code. This proactive methodology detects up to 80% of common programming defects, including unclosed brackets, missing semicolons/colons, unhandled promise rejections, type coercion issues, and high-severity security vectors like direct SQL injections and Cross-Site Scripting (XSS), before code ever touches a build pipeline or production server.
Dynamic Debugging (Runtimes & Profilers): Evaluates code behavior during live execution. While indispensable for discovering complex state interactions and network timeout quirks, dynamic debugging is computationally expensive and exposes servers to runtime exceptions. Pair static analysis with unit tests to achieve maximum reliability.
Clean Code, Refactoring & Defensive Engineering Principles
- Defensive Programming: Never assume input validity. Always include guard clauses (e.g., verifying array length before division to prevent
ZeroDivisionErroror verifying pointer nullability before dereferencing). - DRY (Don't Repeat Yourself): Consolidate duplicated logic into pure, testable utility functions to prevent divergence bugs when business requirements change.
- SOLID Architecture: Adhere to the Single Responsibility Principle (SRP) so each function or class performs exactly one deterministic task, dramatically reducing side-effect regressions.
- Strict Type Coercion: In dynamically typed runtimes (JavaScript/PHP), always enforce strict equality (
===and!==) and sanitize user input with context-specific helpers (e.g.,esc_html(),absint(), or parameterized queries).
100% Client-Side Privacy Guarantee & Zero Cloud Footprint
Unlike conventional cloud-based debugging services that upload your proprietary source code, internal database queries, and private API tokens to remote third-party AI endpoints, the RiazHub Universal AI Code Debugger Studio executes 100% locally inside your web browser.
All AST lexical parsing, delimiter stack tracking, regex heuristics, code diff calculations, and file downloads are performed deterministically on your machine via vanilla JavaScript and HTML5 Blob APIs. No telemetry, database credentials, or secret algorithms ever leave your browser environment.